RiskCompass · risk register and policy · available
One risk register that enforces your policy by itself
Assess risks in sentences instead of numbers, give every risk an owner and a plan, and let RiskCompass raise a signal the moment someone falls behind. Your policy largely writes itself, along ISO 31000 and ISO 27001.
From €99 a month per organisation, unlimited users. Live within one working day.
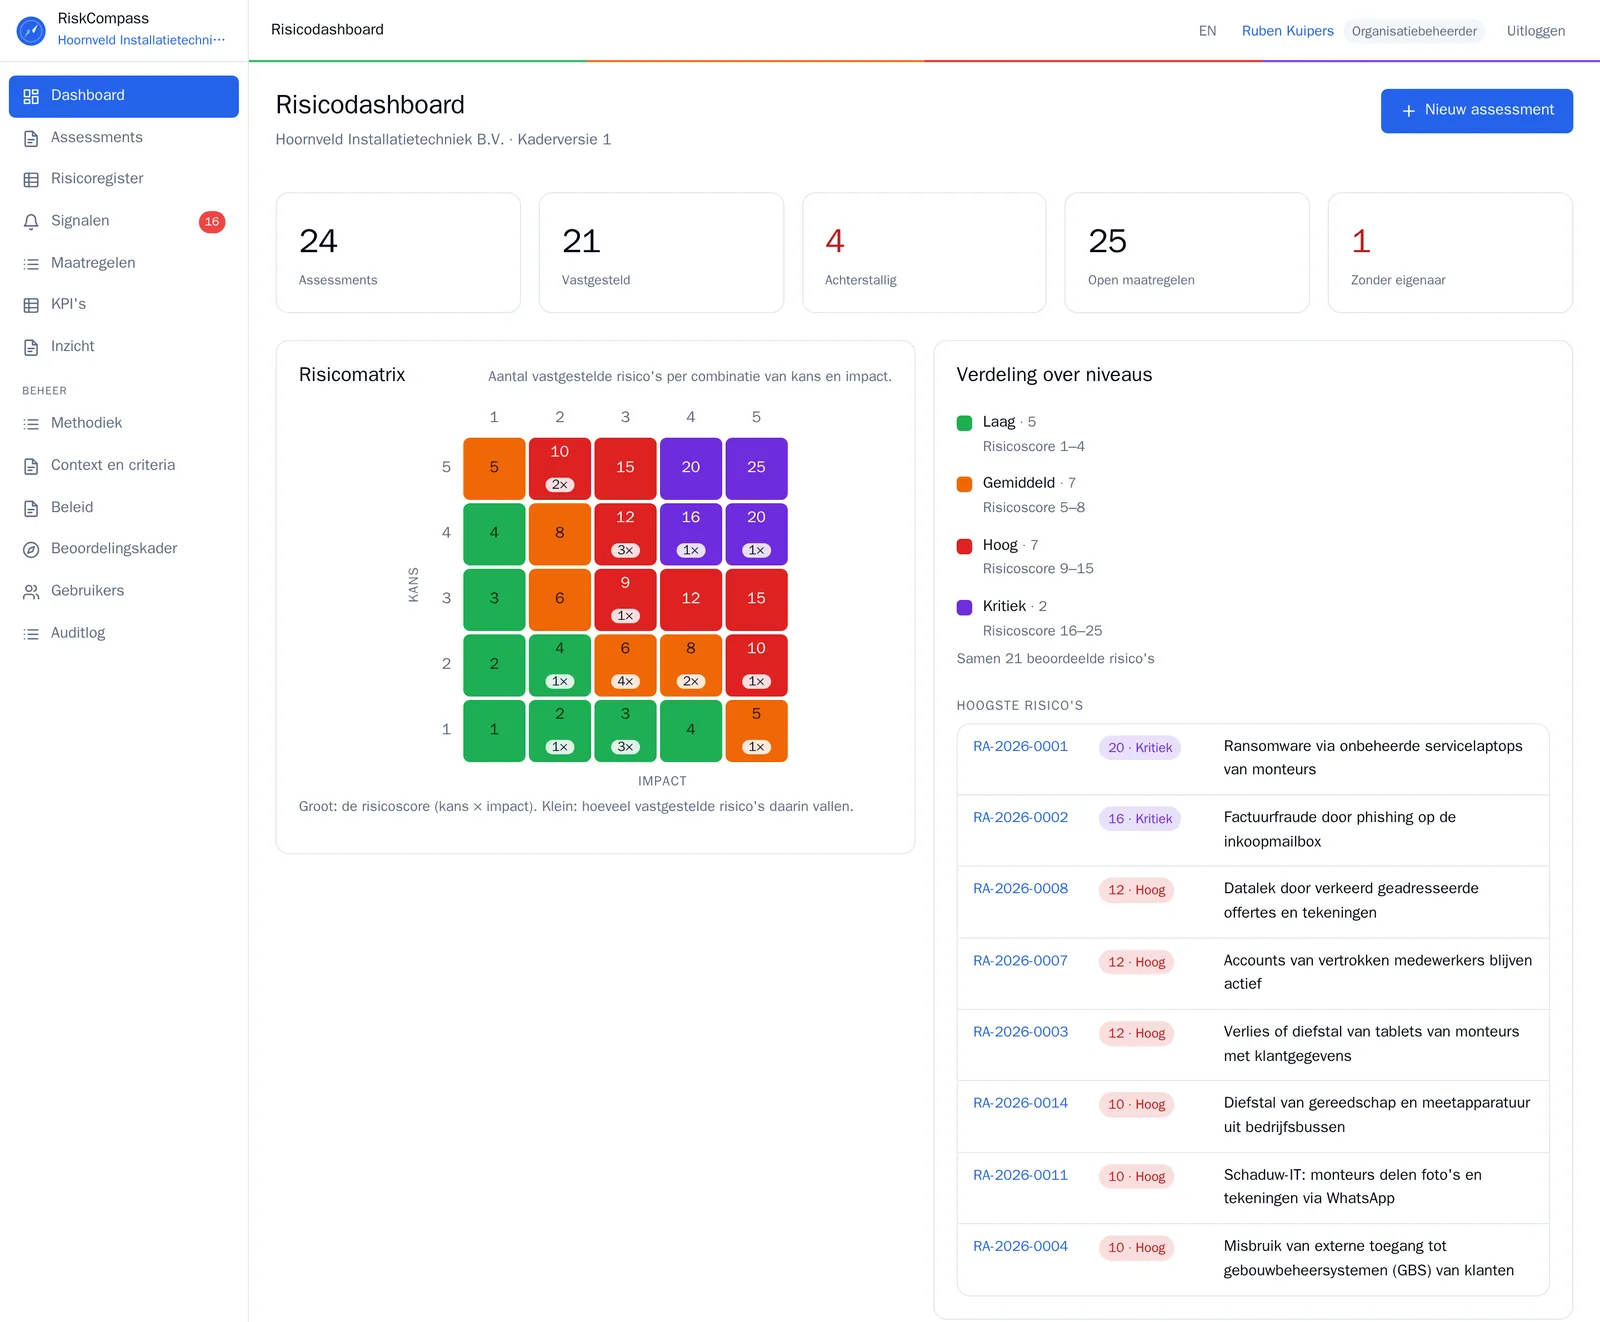
If your environment isn’t ready within one working day, your first paid month is free.
- 8 kinds of signalsrecalculated every day
- 7 of the 11 sectionsof your policy write themselves
- 10 componentsfrom context to monitoring, each in three grades
- Full audit logwho, what, when, from which value to which
From a spreadsheet per risk to one register
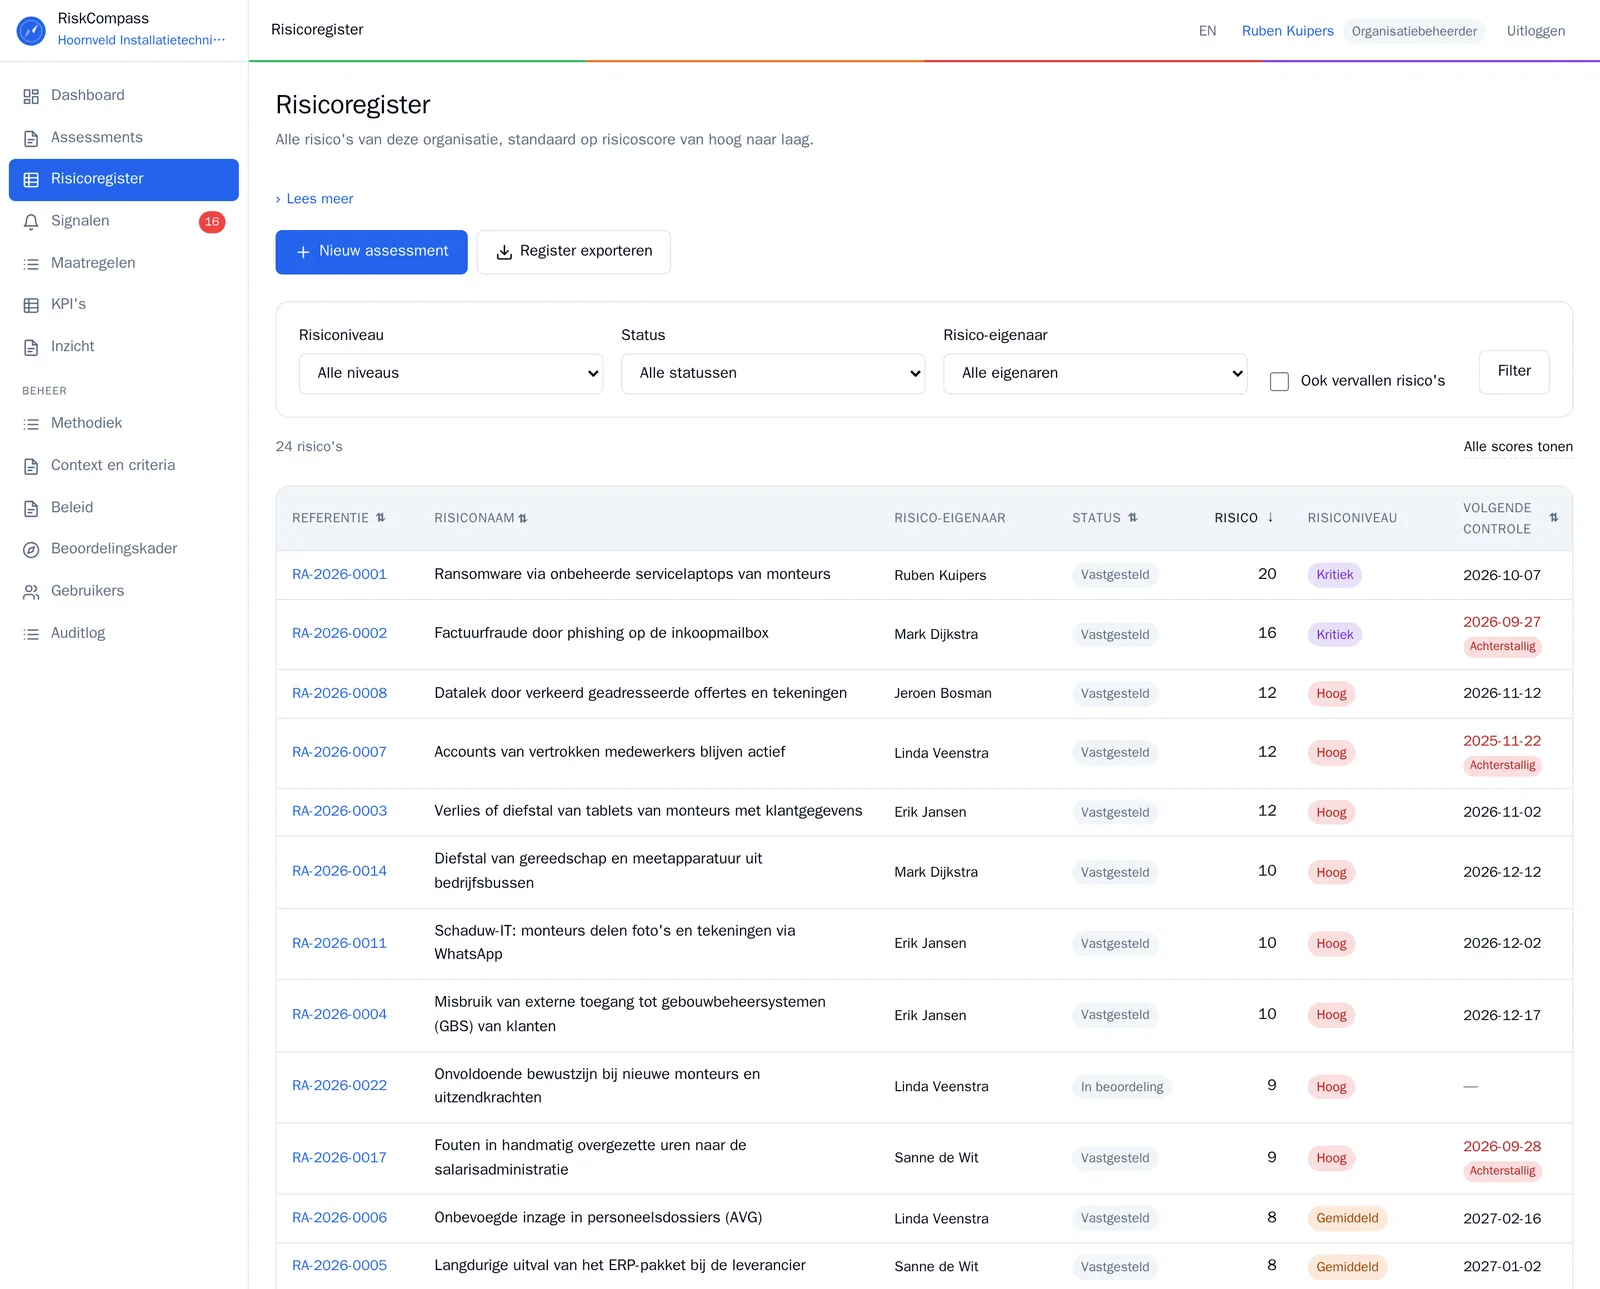
Every risk has a number, an owner, a level, a status and a date for the next review. You can always export to Excel.
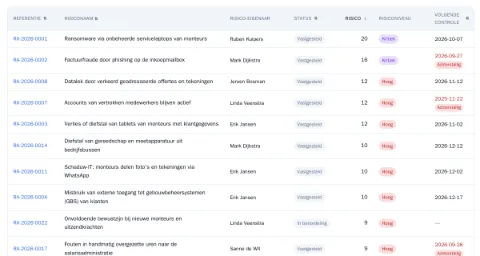
One register
In one list you see what is approved, what is in review and what is still a draft, with the owner and the next review per risk.
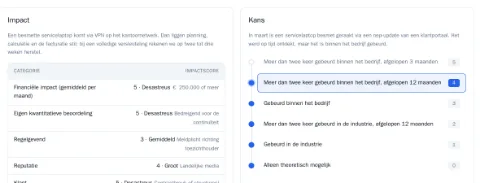
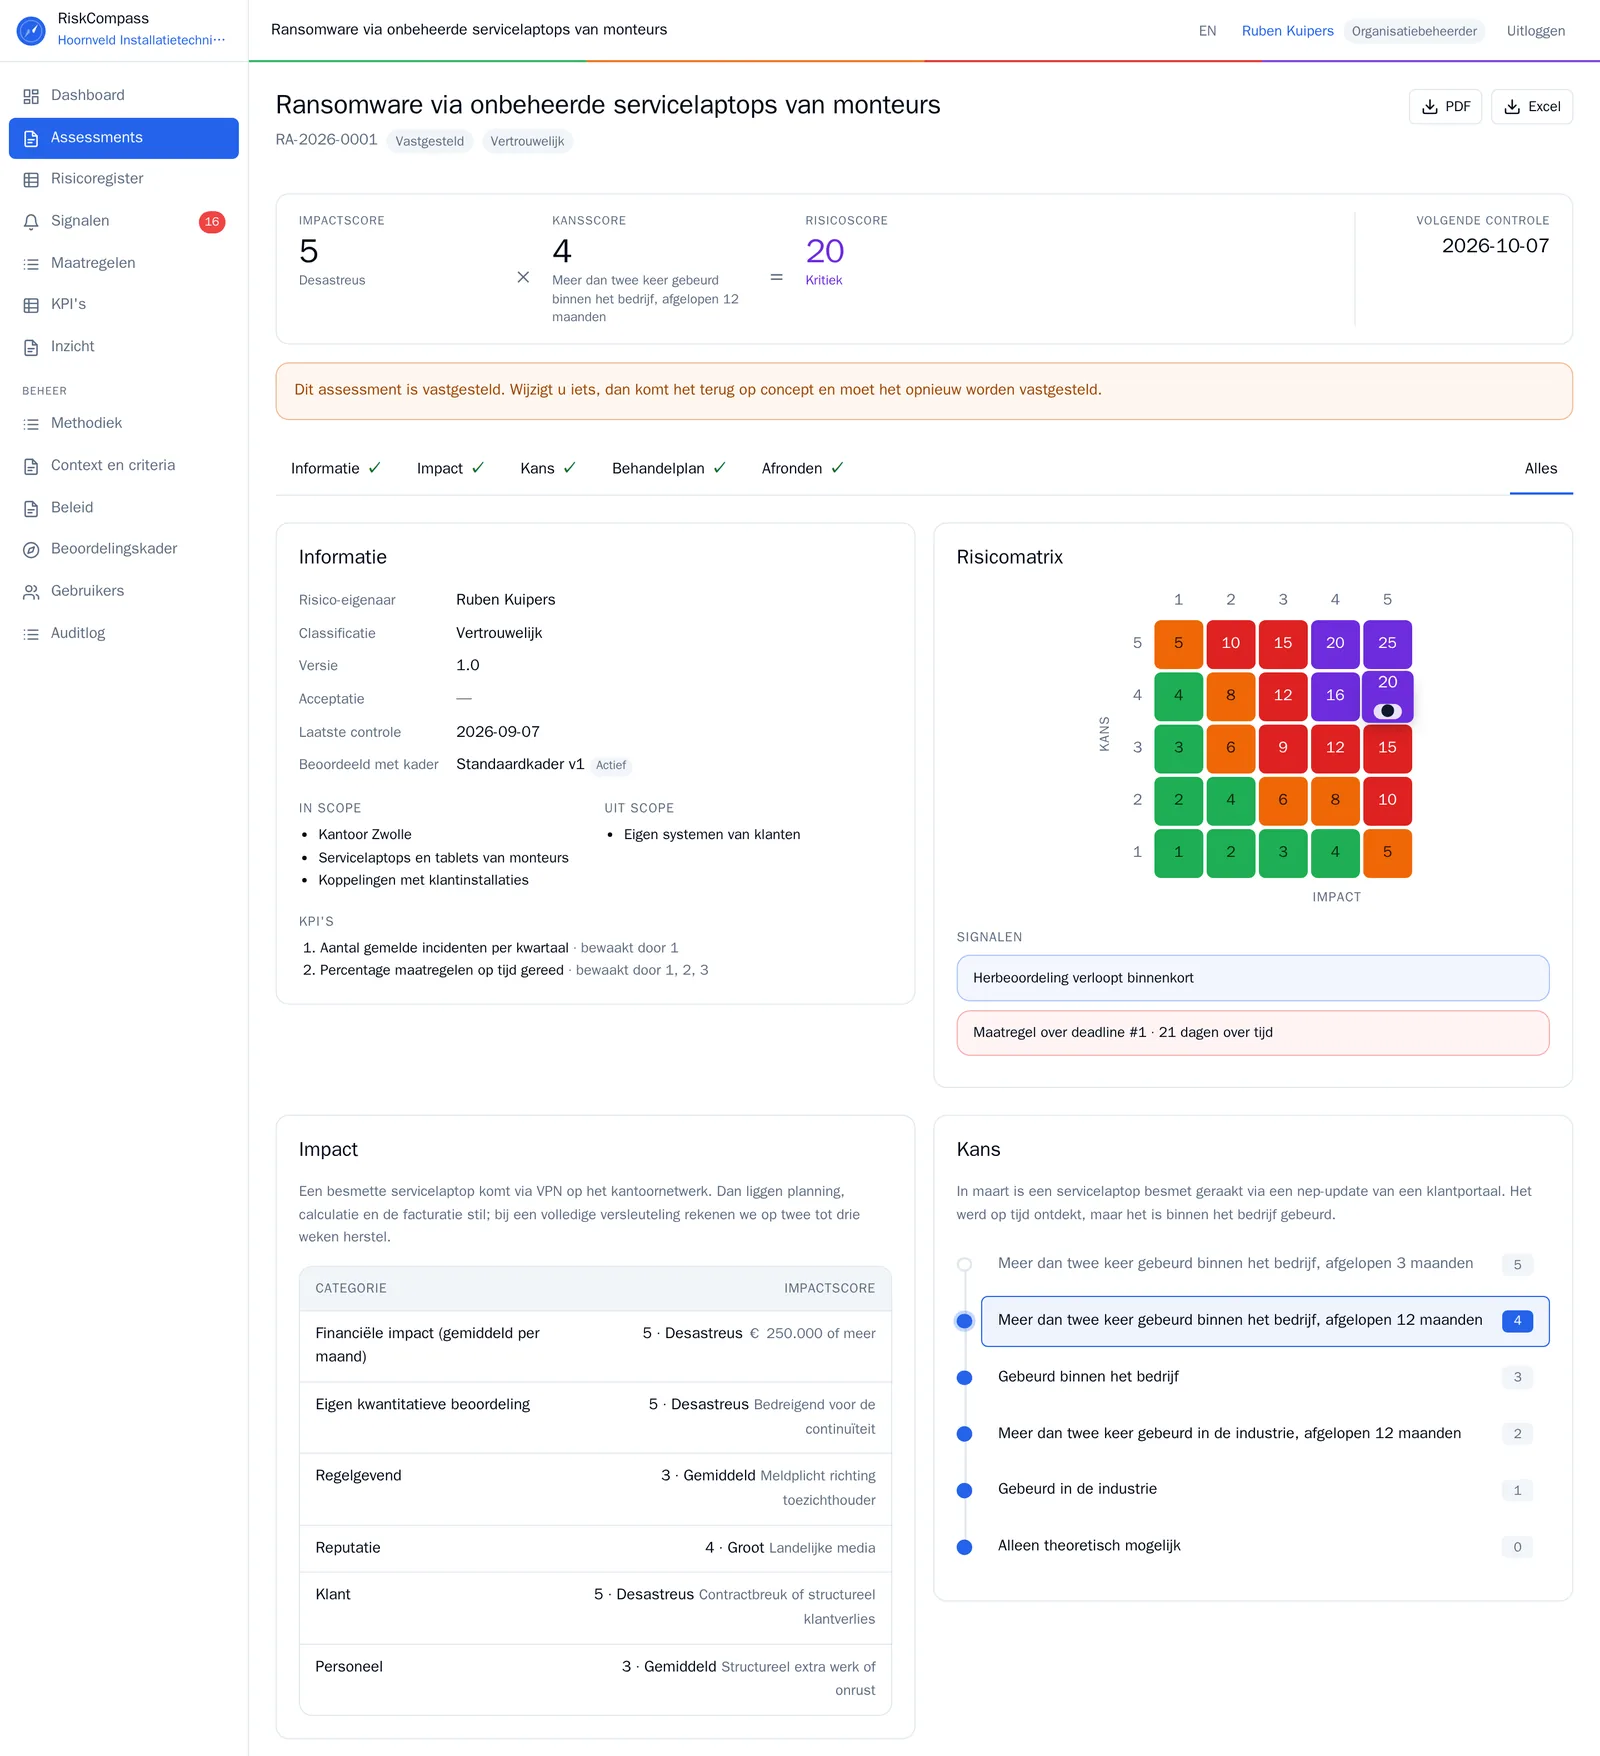
Assess in sentences
For impact and likelihood you pick a sentence rather than a number, such as “more than a week of complete outage”. Two people then weigh the same risk the same way.
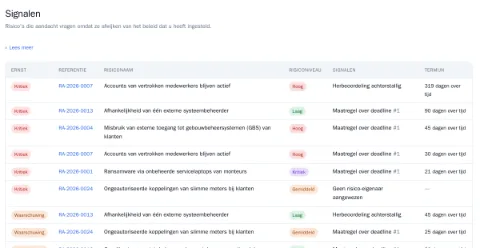
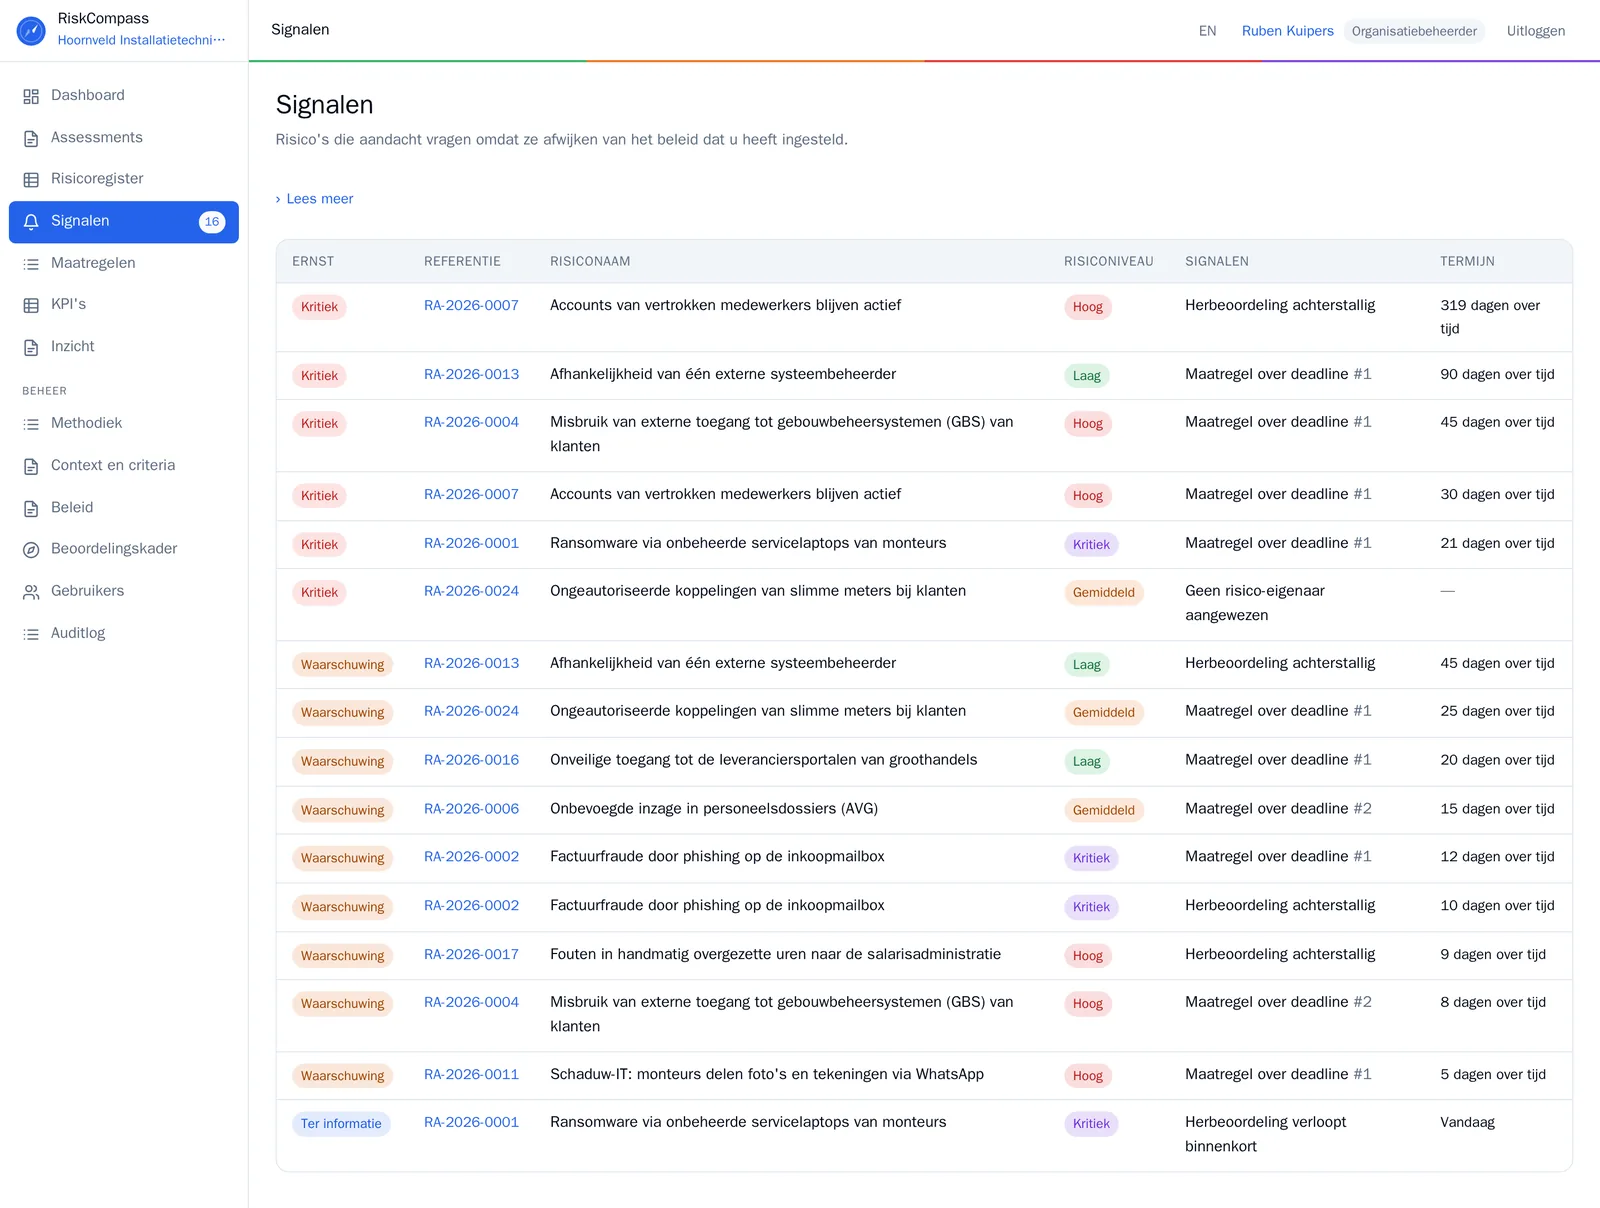
Whoever is behind sees a signal
A reassessment that is late, a plan that is missing, a risk without an owner: it sits at the top for the person who has to resolve it.
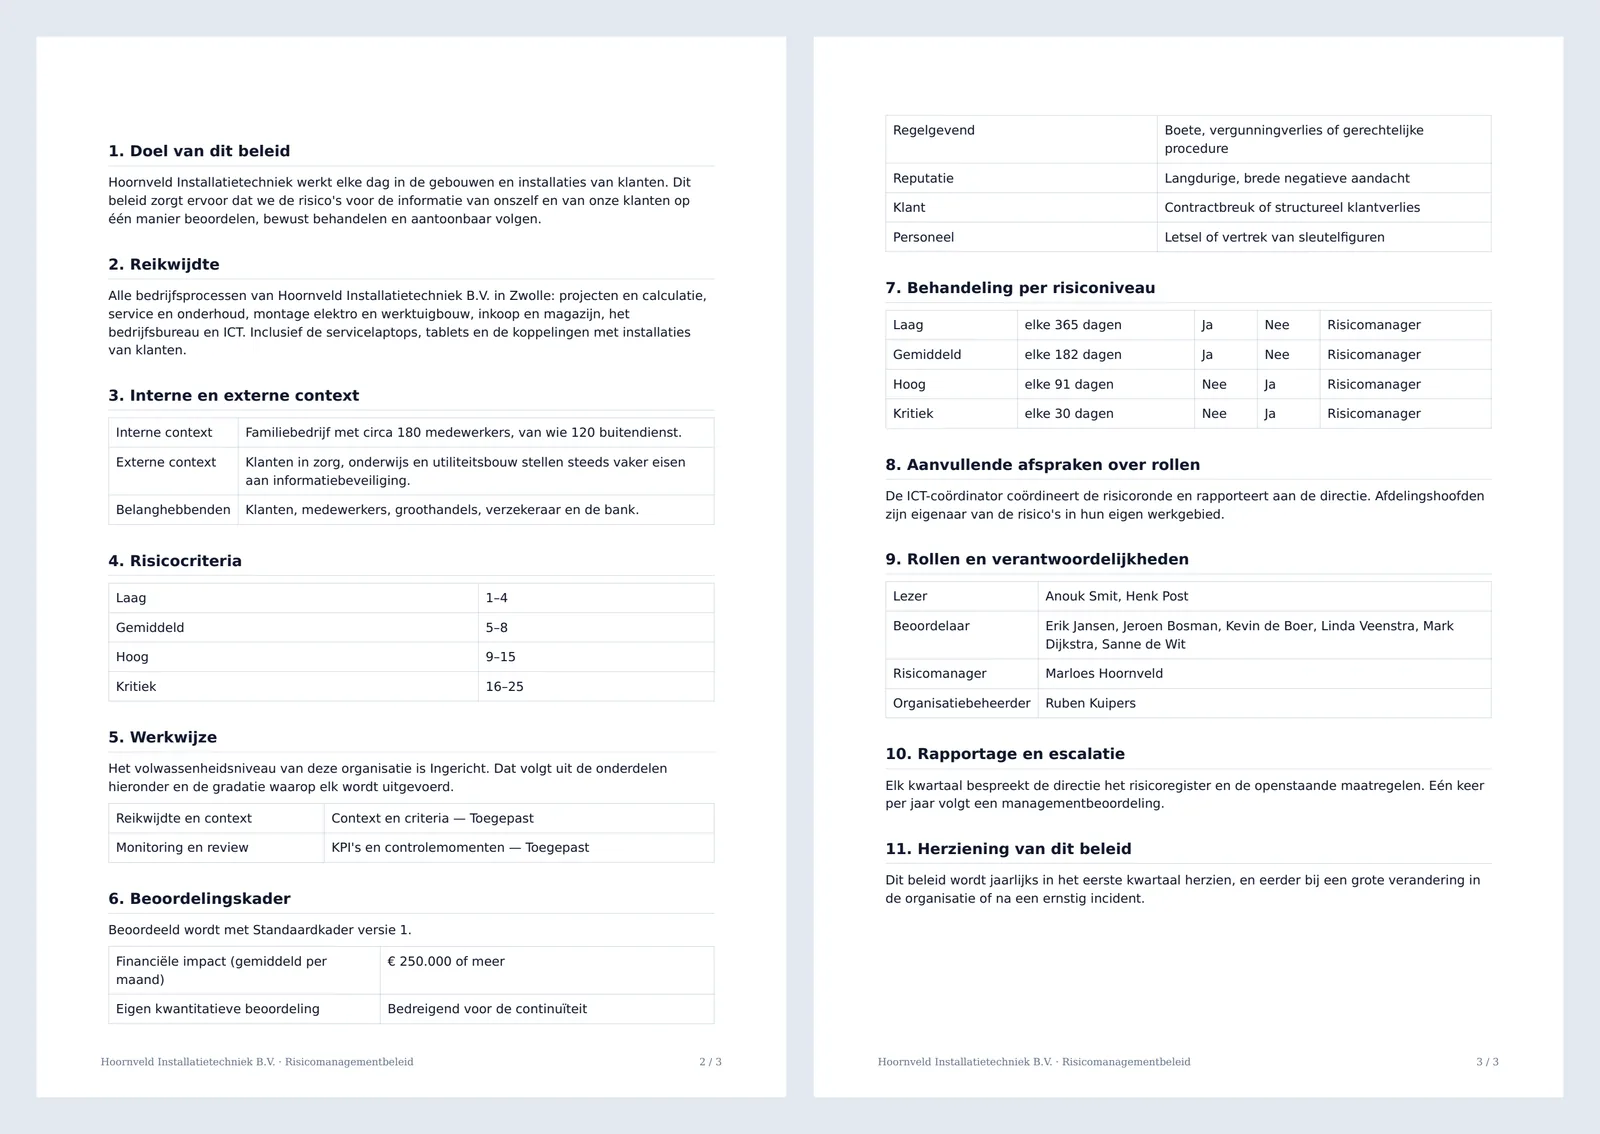
Seven of the eleven sections are already there
The risk management policy and the information security policy largely come from what you have already recorded: your framework, your risk appetite, your roles. Every derived section carries a reference to its source. You approve it and download it as PDF for the auditor and as Word for circulation.
Built on ISO 31000 and the risk requirements of ISO 27001
The six phases of ISO 31000 are the skeleton: context, identification, analysis, evaluation, treatment and monitoring. From ISO 27001, RiskCompass covers the policy (5.2), the risk assessment with an owner (6.1.2), the treatment and residual risk (6.1.3 and 8.3) and the monitoring (clause 9).
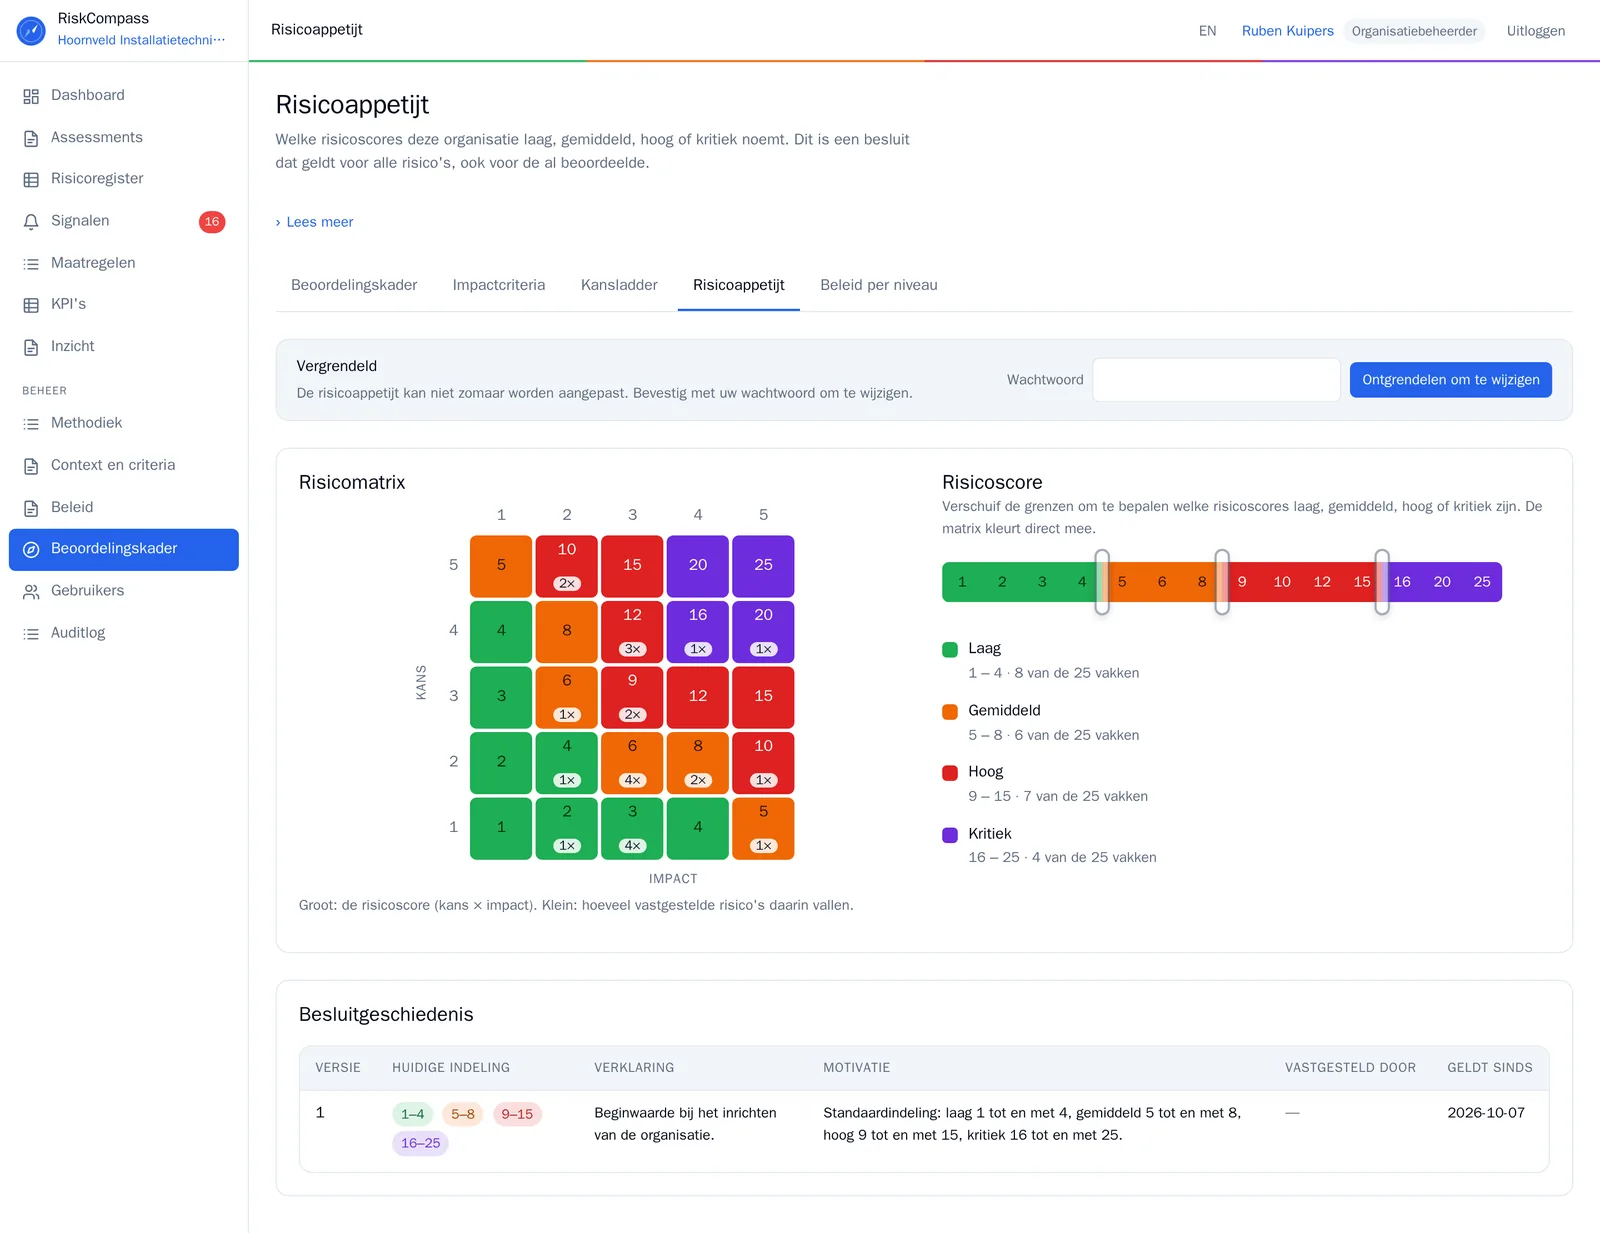
You change the risk appetite only after unlocking with your password. You see beforehand which risks change level, and you record why. Your auditor can read, per risk, who made the judgement, with which framework version and when the next review is due. You paste in your own list of controls and link it to your treatment plans.
Start small, build out when your organisation asks for it
Ten components, from context and assets to bow-tie and Statement of Applicability. You switch on each component at the grade that fits you. The maturity of your risk management follows from what you actually do.
- Treatment plans with measures, deadlines and a KPI per measure, in one overview.
- An assessment framework with versions: a framework in use no longer changes. Editing creates a new version, and every assessment calculates with its own.
- An assessment downloads as PDF or Excel, the policies as PDF or Word. Everything in Dutch or English.
- An audit log of every change: who, what, when, and from which value to which.
- Your data lives in its own environment and is shielded from other organisations inside the database itself.
One price per organisation
By headcount, excluding VAT. How many people work in RiskCompass doesn’t change the price.
| Employees | Per month | Per year |
|---|---|---|
| Up to 50 | €99 | €990 |
| 51 to 250 | €199 | €1,990 |
| 251 to 1,000 | €349 | €3,490 |
Pay annually and you pay for 10 months out of 12. Take Awareness and RiskCompass together and you get 15% off the total. That is the Information security collection.
For your board
Four short sections you can forward: why now, what the risk is, what it costs and what it delivers.
The reason
ISO 27001 asks for a risk assessment with, per risk, an owner, a treatment plan and a reassessment at fixed moments. A customer or an insurer asks how you handle risks too. A spreadsheet per risk doesn’t answer that: nobody sees who is behind, and two assessors weigh the same risk differently.
The risk
A risk without an owner doesn’t get treated, and a judgement nobody repeats goes stale unnoticed. At an audit or after an incident it then turns out the register is wrong. RiskCompass shows that earlier: every risk has an owner, and whoever falls behind sees a signal.
The cost
From €99 per organisation per month, excluding VAT, for an organisation of up to 50 employees. One fixed price by headcount; how many people work in RiskCompass doesn’t change it. Cancel any month, and the first 30 days are free.
What it delivers
One register your auditor can read: per risk who made the judgement, with which framework and when the next review is due. A risk management policy and an information security policy that largely follow from that register, as PDF or Word. And a board that can show its policy is being followed.
Start with RiskCompass before anything else
30 days with your own risks, no payment details. Rather talk first? Pick a time that suits you.